
The Nettko Team is a group of experienced IT professionals passionate about helping businesses grow through smart, innovative technology solutions. Staying ahead of emerging digital trends, they deliver proactive, business-focused IT strategies that enhance agility, performance, and security in today’s fast-changing digital landscape.
How to Safely Roll Out Microsoft Copilot in Your Firm
Key Takeaways
- Inherited Access Controls: Microsoft Copilot mirrors your existing file permissions; if an employee can currently access a document, Copilot can access and utilise content that the user already has permission to view
- Over-Permissioning is the Real Risk: Historical folder sprawl, broad internal sharing links, and public channels create accidental data exposure risks when AI is introduced.
- Governance Before Activation: A secure rollout requires auditing data permissions, establishing sensitivity labels, and reviewing user access before assigning licences.
- Strategic AI Adoption: Combining clear data boundaries with practical staff guidelines allows your firm to harness AI efficiency while protecting client confidentiality.
The Promise and the Hidden Risk of Workplace AI
Microsoft 365 Copilot offers professional services firms a transformative boost in daily efficiency. From drafting complex client correspondence and summarising lengthy documents to analysing financial spreadsheets in seconds, the productivity benefits are substantial.
However, for managing partners, legal directors, and practice managers, introducing an AI engine that scans your firm’s entire document repository brings a critical question: Will Copilot accidentally surface confidential information to staff who shouldn’t see it?
The short answer is yes: if your underlying file permissions are unorganised.
Copilot does not bypass Microsoft’s native security framework. Instead, it respects it precisely. If an employee has technical permission to read a confidential document buried deep within a shared drive, Copilot has permission to read it too. When that employee prompts Copilot with a broad query, the AI can pull insights from executive payroll files, partner strategy notes, or sensitive HR records if those files were improperly shared.
Deploying Copilot safely is not an artificial intelligence challenge; it is a data governance priority.
Why Legacy Folder Structures Create AI Exposure
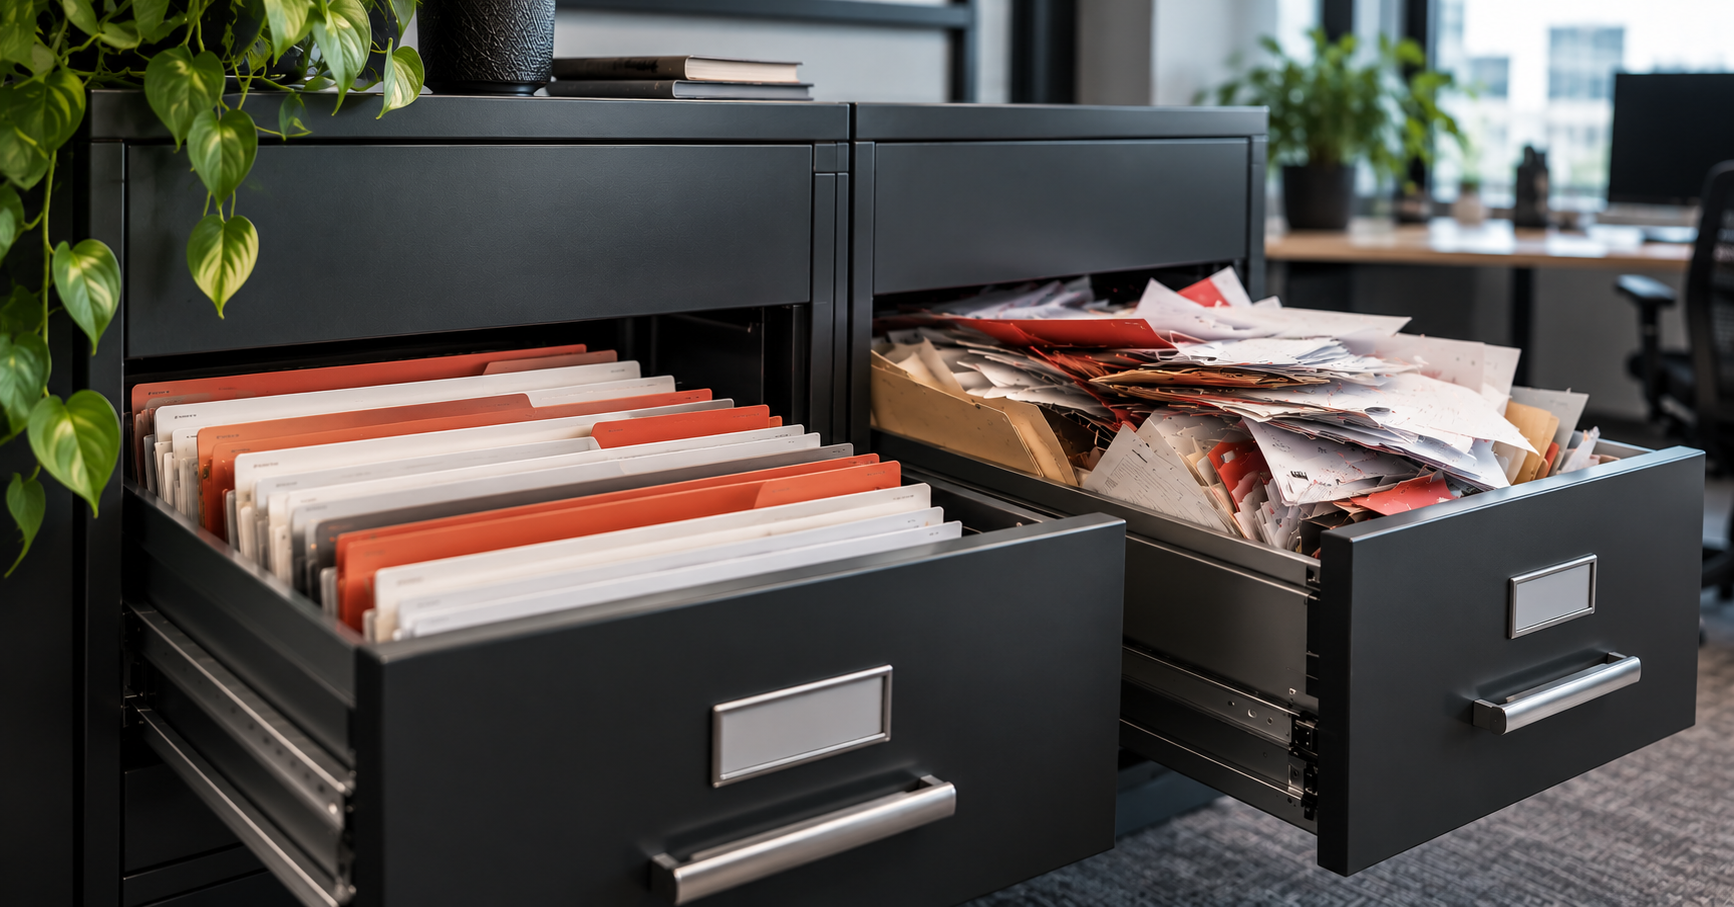
Most professional services firms accumulate years of digital file sprawl. Over time, folder structures grow organically, temporary access permissions get forgotten, and security boundaries erode.
Common permissions oversights that create unexpected AI exposure include:
- Overly Broad Sharing Links: Internal file links created years ago set to “Anyone in the organisation can view,” allowing Copilot to index private documents across the entire business.
- Public Workspace Channels: Collaboration teams created with default “Public” settings instead of “Private,” exposing attached project files and discussion histories to global search.
- Inherited Permission Sprawl: Subfolders inside restricted directories where permissions were modified over time to give temporary access to external parties or junior staff.
- Unrestricted Executive Files: HR files, salary reviews, partnership agreements, and strategic planning notes stored on general shared drives rather than segregated, restricted repositories.
Before assigning Copilot licences to your team, your firm must audit and resolve these legacy security gaps.
A Strategic Framework for Safe Copilot Adoption
To ensure your deployment is smooth, secure, and fully compliant, your technology leadership should follow a structured, four-phase readiness approach.
1. Audit Data Access and Permissions
Review your Microsoft 365 environment to identify files, sites, and directories configured with broad internal access or outdated permissions. Establishing clear visibility over your data landscape is the essential first step.
2. Clean Up Over-Permissioned Data
Restructure access boundaries so staff members only have access to the specific folders and client records strictly required for their roles. Revoke outdated organisational sharing links and convert open workspaces to restricted access where appropriate.
3. Apply Data Classification and Sensitivity Controls
Utilise built-in Microsoft security features to classify sensitive documents (such as Confidential or Executive Only). Sensitivity labels, retention controls and data access reviews help reduce the risk of sensitive information being surfaced inappropriately.
4. Assess Copilot Readiness
Conduct a structured readiness assessment to evaluate your Microsoft 365 environment before deployment. Review data locations, external sharing settings, governance controls, and security configurations to identify potential exposure risks and remediation priorities. A readiness assessment helps ensure your organisation is prepared to gain value from Copilot while maintaining appropriate safeguards.
5. Pilot Copilot with a Controlled User Group
Begin deployment with a small group of trusted users representing different business functions. A pilot program allows your organisation to validate permissions, test governance controls, identify unexpected access patterns, and gather practical feedback before expanding adoption across the broader workforce.
6. Establish Clear Staff Usage Guidelines
Technology controls must be paired with clear human guidelines. Provide your team with practical policies regarding what types of data can be processed using AI, the requirement for human review of all AI-generated outputs, and the importance of maintaining client privacy.
Final Thoughts
Rolling out Microsoft Copilot should be an exciting step forward in operational efficiency, not a source of executive anxiety.
The primary risk to your firm’s confidentiality is not the AI technology itself—it is the unorganised data permissions currently sitting in your cloud environment. By prioritising data governance, cleaning up legacy access rights, and establishing clear usage guidelines, your business can adopt Microsoft Copilot with complete confidence.
Planning to launch Microsoft Copilot in your firm?
Book a Microsoft Copilot Readiness Assessment with Nettko today. We will help you review your Microsoft 365 environment, organise your permissions, and ensure your data remains completely secure before you activate your AI licences.